Turn Your ISO 27001 Certification into a Trust Asset
Communication Guidelines
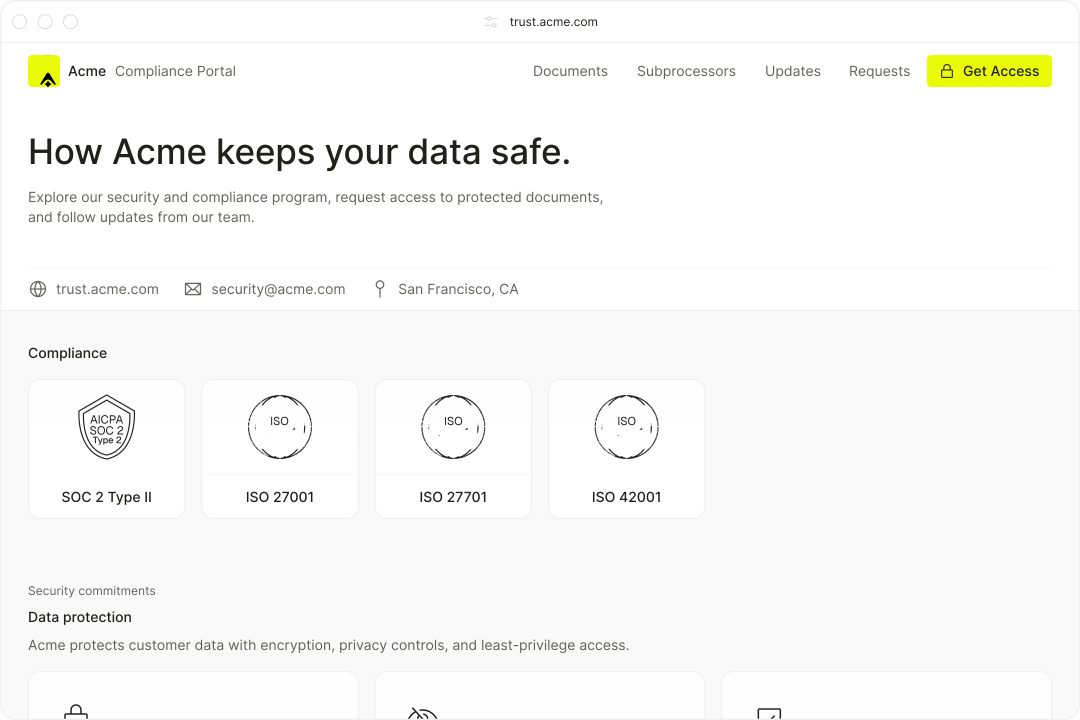
Trust center
Create or update your Trust Center to showcase your new ISO 27001 certification.
You don't have a Trust Center yet?
Reach out to the ZebraByte team, we will get yours for free.
Example

Achievement
Value for Customers
Linkedin post & blog article content
Linkedin post
It is now a good time to inform your customers and prospects about your new milestone.
We recommend you to start by posting it on your Linkedin page (if you tag ZebraByte we will be glad to share it).
Here is an example you can use:
🔐 We're Now ISO 27001 Certified
Security and trust have always been core to how we build and operate. Today, we're proud to share an important milestone: we've achieved ISO/IEC 27001 certification, the international standard for information security management system (ISMS).
This isn't just about passing an audit. It reflects the systems, processes, and culture we've put in place to manage risk, protect sensitive information, and continuously improve how we safeguard our customers' data.
For our customers and partners, this means:
- A structured, risk-based approach to information security
- Strong governance across people, processes, and technology
- An ongoing commitment to protecting what matters most
👏 A big thank you to @ZebraByte, whose platform and team made the entire ISO 27001 journey significantly smoother.
And of course, huge thanks to everyone internally who contributed to making this happen.
Linkedin asset template
You can download and customize this template to visually support your post, if needed.
Blog article
We advise you to create a page about your ISO 27001 certificate to
give context to your customers and prospects.
You can also link this page to the ISO badge display on your
website.
✏️
[Company Name] Achieves ISO/IEC 27001 Certification, Strengthening Its Commitment to Information Security
We're proud to announce that [Company Name] is now ISO/IEC 27001 certified, marking a major milestone in our ongoing commitment to protecting information and earning the trust of our customers and partners.
This achievement reflects the work we've done to build security into how we operate. First, across our people, processes, and technology. And continuously, to manage information security risks in a structured and transparent way.
This milestone was achieved in close partnership with ZebraByte, whose platform and team guided us through the ISO 27001 journey and helped make the process significantly smoother from start to finish.
What this means for our customers
ISO/IEC 27001 certification provides independent validation that [Company Name] has implemented and operates a robust Information Security Management System (ISMS) aligned with international best practices.
For our customers, this means:
- Increased confidence in how we protect sensitive and confidential information
- A risk-based approach to identifying and managing information security threats
- Easier vendor security assessments and procurement reviews
- Alignment with enterprise, regulatory, and contractual security expectations
- Assurance that security is embedded into our daily operations
ISO/IEC 27001 is not a one-time effort. It represents a continuous commitment to maintaining, monitoring, and improving our information security practices over time.
What is ISO/IEC 27001, exactly?
ISO/IEC 27001 is the leading international standard for information security management, published by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC).
The standard defines requirements for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). This system is designed to help organizations systematically manage information security risks, taking into account:
- People and organizational processes
- Technology and infrastructure
- Legal, regulatory, and contractual obligations
As part of the certification process, an independent, accredited certification body audited our ISMS and verified that it meets the requirements of ISO/IEC 27001 within the defined scope of certification.
A structured, ongoing approach to security
Achieving ISO/IEC 27001 certification required us to formalize and strengthen how we approach information security, including:
- Identifying and assessing information security risks
- Defining and implementing appropriate security controls
- Establishing clear governance, policies, and responsibilities
- Continuously monitoring, reviewing, and improving our security posture
You can access our ISO 27001 Certificate here: [link to your trust center]
Assets for your website
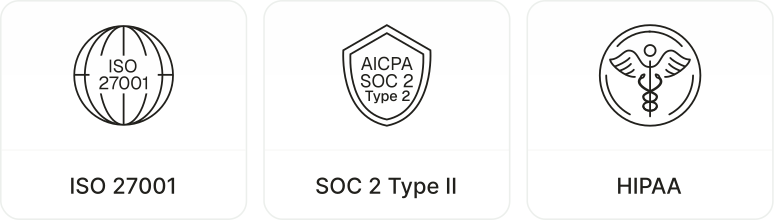
Compliance Badges for ISO 27001
ZebraByte logo
Add the ZebraByte logo next to your compliance badge to highlight your certified status.


Turn compliance into business growth
Turn ISO 27001 into a sales accelerator
Proactively mention ISO/IEC 27001 early in sales conversations or outbound messages.
Reduce security questionnaires by pointing prospects to your ISO/IEC 27001 certification and scope statement.
This can significantly shorten enterprise security reviews.
Make certification a competitive advantage
If competitors are not ISO 27001 certified: mention it explicitly in competitive deals.
Website placement
Add ISO 27001 (small badge or text) signals in:
- Website placement
- Footer
- Security / Trust page
- Pricing or Enterprise page
- Signup pages
Example

Inform & train your team (sales and CS)
Share with them this guideline.
Make sure they can confidently answer:
Strengthen customer retention & expansion
Announce ISO/IEC 27001 certification to existing customers:
- Customer newsletter
- In-app notifications
Position it as:
"An investment we made to protect your information as you grow with us."